
AI Procurement Workflow Automation: Where to Keep Human Approval
TIME
Click count
AI Procurement Workflow Automation: Where to Keep Human Approval
The search for “ai tools for automating procurement workflow best practices” often comes down to one practical question: which decisions should people still own? AI can accelerate purchase requests, supplier comparisons, and invoice matching, but speed should not override accountability. For procurement operators, the priority is knowing where automation can proceed safely and where human approval remains essential—especially for high-value purchases, supplier changes, and policy exceptions. This guide explains how to place approval checkpoints, handle exceptions, and maintain audit trails without turning every transaction into a bottleneck.
Separate preparation from permission
Procurement automation becomes easier to control when the workflow distinguishes between preparing a decision and authorizing an action. Extracting payment terms from a quotation is preparation. Accepting those terms is a commitment. Identifying a possible duplicate invoice is analysis. Releasing payment is an authorized financial action.
AI is useful for reading inconsistent documents, classifying requests, summarizing bids, and explaining discrepancies. Those capabilities do not make it an appropriate approval authority. Use a controlled rules engine to enforce spending limits, approved supplier status, required documents, and segregation of duties. Let AI interpret information within that structure, rather than rewrite the structure as it works.
For routine purchases, automation can continue without a fresh human click when existing policy explicitly permits it. A repeat catalog order within an approved budget may qualify. An apparently similar order with a new delivery location, changed specification, or expired contract may not. Eligibility for automatic processing should depend on verified conditions, not simply on how confident the model sounds.
Place approvals where the business takes on risk
Start with the points where money, obligations, supplier access, or operational exposure change. These boundaries usually deserve more attention than every intermediate document update.
Before committing spend or accepting changed terms
Keep accountable approval for purchases outside delegated authority, unbudgeted requests, and material changes to an approved commitment. Assess the total commitment, including recurring fees, implementation costs, freight, and other applicable charges—not just the amount on the first invoice. Check related requests where splitting could bypass a threshold.
Value alone is insufficient. A low-cost SaaS subscription may involve sensitive business data. An inexpensive replacement component may affect machine safety or warranty coverage. Route these decisions to the relevant technical, security, or legal owner rather than assuming procurement approval covers every risk.
Before onboarding suppliers or changing payment details
AI can assemble onboarding files, flag missing fields, and compare names across records. Keep human approval for activating a supplier where due diligence is required, and for changes to bank details or payment instructions. Verify sensitive changes through an independently established contact channel, not the contact information supplied in the change request itself.
Separate the person requesting a supplier-master change from the person approving it. A convincing email, complete form, or familiar logo is not independent verification. Automated document checks can support that control, but should not replace it.
Before waiving a control or resolving a material discrepancy
Single-source exceptions, retrospective purchase orders, missing receipts, and invoices outside approved tolerances need a named decision-maker. The approval should explain why the exception is acceptable and what evidence supports it. “Urgent” describes timing; it does not establish authority.
For invoice processing, distinguish ordinary matching from exception resolution. An invoice that matches an approved purchase order and confirmed receipt may proceed under established controls. A quantity discrepancy should go to the receiving owner. A price variance may require the buyer. Payment release remains subject to separate treasury or finance authorization, even after matching is complete.
A workable flow is: request capture → document extraction → policy checks → automatic processing or assigned approval → authorized execution → reconciliation. Place the exception queue beside this flow, with clear return points, rather than letting unresolved items disappear into email.
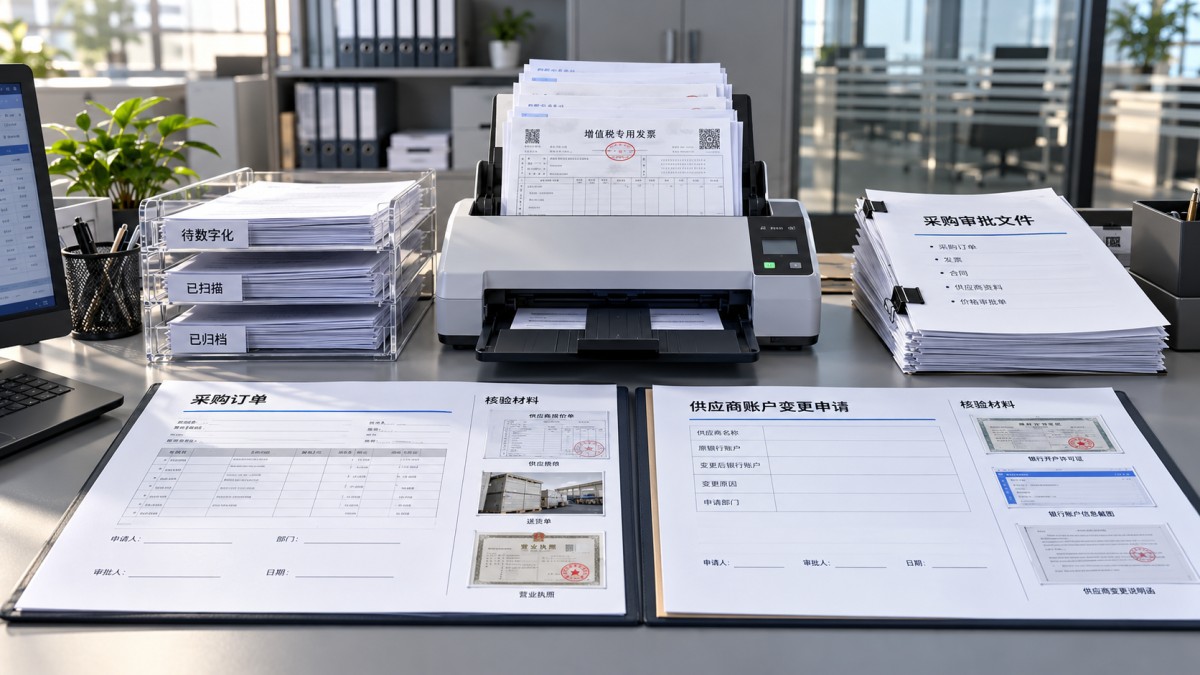
Build an approval packet people can actually review
An approval button beside an AI summary is not enough. Reviewers need to see the proposed action, its business consequence, and the source evidence without reconstructing the transaction themselves.
- Decision requested: approve the order, accept a variance, activate a supplier, or authorize a specific exception.
- Financial scope: total commitment, currency, budget owner, and the relevant approval authority.
- Evidence: linked quotation, contract clause, receipt, supplier record, or invoice passage supporting the recommendation.
- Unresolved issues: conflicting documents, missing information, and assumptions that require confirmation.
- Reason for routing: the exact policy condition or discrepancy that triggered review.
For supplier comparisons, preserve the distinction between facts and judgments. Delivery lead time quoted by a supplier is a source claim. A recommendation that the supplier offers lower operational risk is an assessment. Reviewers should be able to inspect the criteria and weighting behind that assessment, especially when price, service coverage, and specification compliance point in different directions.
Approval should bind to a specific transaction version. If bank details, quantity, price, scope, or material terms change afterward, evaluate whether reapproval is required. Otherwise, a legitimate approval can end up attached to a different purchase.
Treat uncertainty differently from policy exceptions
A blurred invoice and an unauthorized purchase are not the same problem. The first may need document correction; the second needs an accountable business decision. Sending both to a generic “manual review” queue creates avoidable delays and hides the reasons automation stops.
Use separate routes for incomplete data, commercial discrepancies, policy exceptions, and suspected fraud. Give each route an owner, required evidence, and escalation path. When information is missing, return a precise request—such as “confirm received quantity”—rather than asking someone to review the entire transaction.
Do not turn a model confidence score into a universal approval threshold. Extraction confidence does not establish supplier legitimacy, contractual acceptability, or budget authority. Test confidence signals against representative documents and actual errors before using them to route work.
Approval deadlines also need boundaries. Reminders and escalation to an authorized delegate are reasonable. Silent approval because someone did not respond is a poor default for material risk. Emergency purchasing should follow a documented alternative route, not an informal bypass hidden inside the automation.
Check what the tool can execute, not just what it can read
A procurement copilot that drafts a comparison has a different risk profile from an agent that can edit supplier records or issue purchase orders. Evaluate permissions at the action level. Reading a contract should not automatically grant the ability to accept it; drafting an order should not grant permission to transmit it.
Supplier documents and emails should be treated as untrusted input. Embedded instructions must not be able to override approval rules or trigger tool actions. Enforce authorization outside the language model, restrict integrations to necessary operations, and require validated inputs before execution.
During evaluation, ask vendors to demonstrate a changed bank account, a duplicated submission, an unavailable approver, and a failed ERP connection. Watch whether the system blocks safely, preserves the work, and avoids creating duplicate orders when retried. A polished document-extraction demonstration will not reveal these operational weaknesses.
Also confirm how supplier pricing, contracts, and personal information are retained, accessed, and used by the provider. Appropriate arrangements depend on the information involved, contractual obligations, and applicable local requirements.
Keep an audit trail that explains the decision
A useful record connects the original evidence, extracted fields, applicable policy version, AI recommendation, human decision, and executed action. Capture who approved, their authority at that time, any delegation, and the reason for an override. Retain relevant model and workflow versions so later reviewers can understand how the result was produced.
Logging is not the same as accountability. Assign an owner to review exceptions and investigate patterns, including repeated overrides, requests clustered below approval limits, or unusual supplier-master changes. Protect records from unauthorized alteration and set retention according to business and applicable legal requirements.
Pilot a narrow workflow before expanding authority
Begin with stable, repeatable transactions involving approved suppliers and clear supporting records. Run AI recommendations in shadow mode, comparing them with operator decisions before enabling execution. Include difficult documents and known exceptions in testing; clean invoices alone provide little assurance.
Track more than processing speed. Measure incorrect automatic routing, missed exceptions, reviewer rework, duplicate actions, and time spent waiting for missing evidence. Review rejected recommendations as well as accepted ones. Define who can pause automation and how work returns to a controlled manual process.
Cross-industry intelligence helps identify where that pilot boundary belongs. The Global Industry Synergy Network (GISN) connects industrial analysis with global trade context across energy, machinery, digital SaaS, building materials, and travel. Across these sectors, the approval concern may shift from technical compatibility to data access, delivery obligations, or cancellation terms. Market insight can inform those checks; it does not replace transaction-level verification.
Before expanding automation, write down three things for each action: the conditions permitting automatic execution, the event requiring human approval, and the person authorized to make that decision. If any of those remain ambiguous, keep the action in recommendation mode until the boundary is clear.
Recommended News
- AI Procurement Workflow Automation: Where to Keep Human ApprovalOct 21, 2026Explore ai tools for automating procurement workflow best practices: discover where to keep human approval, reduce risk, and accelerate purchasing with smarter controls.
- How Can You Verify an AI Vendor Has Real Manufacturing Data?Oct 12, 2026How to verify if an AI tool vendor has real manufacturing data: discover provenance checks, legal safeguards, and factory-fit tests to avoid costly mistakes and choose with confidence.
- Do AI Manufacturing Inspection Tools Actually Reduce Inspection Time?Sep 16, 2026Do AI tools for manufacturing actually reduce inspection time? Discover where AI vision saves time, what affects ROI, and how to pilot smarter quality control.
- How Intelligent Data Analysis Dashboards Turn Operational Data Into Actionable DecisionsAug 30, 2026Intelligent data analysis dashboard: turn project data into clear, timely actions. Spot risks, control costs, protect schedules, and improve operational decisions.
- EU AI Act Article 50 Takes Effect, Requiring Clear Labels on AI-Generated ContentAug 15, 2026EU AI Act Article 50 now requires clear labels on AI-generated content in EU markets—learn what this means for listings, customer service, and compliance risks.
- TBEA’s 29 New Energy and Power Equipment Products Pass National-Level AppraisalOct 26, 2026TBEA’s 29 new energy and power equipment products reportedly passed national-level appraisal. Explore the results and key checks for smarter procurement decisions.
- Baby Sleeping Bags: Choosing the Right TOG Rating and a Safe FitOct 25, 2026Choosing babysleepingbags? Discover how to match TOG ratings to room temperature, check for a safe fit, and avoid overheating with practical tips to help you shop confidently.
- Eco Building Solutions in the UAE: Estidama vs. Al Sa'fat RequirementsOct 21, 2026Explore eco building solutions UAE projects need. Compare Estidama and Al Sa’fat ratings, technical requirements and compliance evidence to reduce approval risks and choose with confidence.
- CE Marking: How to Identify Your Product Category and Applicable EU RulesOct 19, 2026Explore product category analysis CE assessors can use to identify applicable EU rules, resolve overlapping obligations, and plan conformity assessment before costly testing.
- What Drives the Cost of Technical Specification Analysis Before Procurement?Oct 14, 2026Understand technical specification analysis cost before procurement. Explore key cost drivers, compare review scopes, and reduce unnecessary spend without compromising purchasing confidence.
- Outdoor Furniture Prices by Material: Purchase, Delivery, and Upkeep CostsOct 27, 2026Compare outdoor furniture price by material, including purchase, delivery, and upkeep costs. Discover how to evaluate supplier quotes and choose better long-term value.
- Real-Time Industrial Trend Analysis: Which Indicators Signal Demand Shifts?Oct 23, 2026Use real time industrial trend analysis to spot demand shifts early. Discover how orders, inventory, and factory activity reveal buying signals and guide smarter business decisions.
- Global Sourcing for Procurement: How to Compare Total Landed CostsOct 22, 2026Optimize global sourcing for procurement by comparing total landed costs, from freight and duties to quality risks. Discover how to uncover hidden costs and choose suppliers with confidence.
- How Can Data Analysis Compare Global Supplier Pricing Trends?Oct 12, 2026How to use data analysis to compare global supplier pricing trends? Learn to align quotes, track currency impacts, and compare landed costs for smarter sourcing decisions.
- Vietnam Precast Concrete Market: Demand Drivers, Capacity, and Buyer RisksOct 09, 2026Vietnam precast concrete market insights: assess demand drivers, production capacity, logistics, quality compliance, and buyer risks for smarter sourcing and investment decisions.
All Categories
Hot Articles
- Outdoor Furniture Prices by Material: Purchase, Delivery, and Upkeep CostsOct 27, 2026Compare outdoor furniture price by material, including purchase, delivery, and upkeep costs. Discover how to evaluate supplier quotes and choose better long-term value.
- Chile’s BESS Cut Curtailment as Projects Under Construction Are Expected to Triple CapacityOct 27, 2026Chile’s BESS are cutting renewable curtailment, while ACERA expects projects under construction to triple storage capacity. Explore what this could mean for developers and suppliers.
- Energy Management in North America: Using Demand Response to Cut Facility CostsOct 26, 2026Explore energy management North America facilities can use to cut costs with demand response. Learn to assess programs, protect operations, and unlock reliable savings.